

Authorised Importer of  for Australia / New Zealand
/ Cloud Security Solutions

Insecure changes cost far less to fix before they reach production. You have to actively hunt for toxic combinations of permissions, like a developer role that https://ustechsregister.com/best-computer-spy-app-of-2019-theonespy.html can both create a resource and approve its own access request, before someone else exploits them. This means creating reference architectures for your cloud networks, identity models, and landing zones, and enforcing them through infrastructure-as-code templates instead of one-off builds. You cannot expect teams to configure everything perfectly from memory every single time they spin up a server. The practices below describe what mature enterprise security looks like in reality.

These are ideal for detecting and correcting misconfigurations before they become significant problems in the future. Certification ensures consistent application of encryption, access control and risk management policies across all https://trash-removal.org/hometrash/cincinnati-trash-pick-up.html cloud assets. Attackers target enterprises for their data scale, complex architectures and often-fragmented security governance. Enterprise cloud security encompasses the strategies and technologies that protect enterprise applications, workloads and data hosted in cloud environments.

Additionally, security teams have limited visibility into workloads running on public cloud offerings, making it more difficult to ensure protection. Public cloud services are delivered by a third-party provider from a virtualized pool of resources where multiple customers or tenants may be renting computing resources on the same physical server. Immature application security programs without clear governance drive higher remediation costs and slower delivery. Inconsistent configurations across Azure, AWS, and Google Cloud Platform create fragmented visibility and compliance risk. PwC’s Enterprise & Cloud Security practice helps clients address these challenges through integrated services spanning cloud architecture, network and OT security, and application protection.
CNAPP Market Guide
The way to approach cloud security is different for every organization and can depend on several variables. Regardless of the preventive measures organizations have in place for their on-premises and cloud-based infrastructures, data breaches and disruptive outages can still occur. The core functionality of IAM is to create digital identities for all users so they can be actively monitored and restricted when necessary during all data interactions. A substantial portion of breached records can be attributed to misconfigured assets, making the inadvertent insider a key issue for cloud computing environments. Overall accountability for data privacy and security still rests with the enterprise, and heavy reliance on third-party solutions to manage this component can lead to costly compliance issues.
That’s why rolling out efficient cloud security measures is critical to staying compliant and clear of these pitfalls. Fall short of these rules, and you’re looking at hefty fines, more financial damage, and a major trust deficit with customers and business partners. It’s a vast field that calls for a layered strategy and a good understanding of the shared responsibility model – a model where both the cloud provider and the user have a part to play in securing the cloud. Whether your organization is in the middle of moving to the cloud or seeking to improve your current cloud security stance, this guide acts as a handy reference. This guide will deliver a detailed breakdown of Enterprise Cloud Security, delving into its various elements, recommended practices, and emerging trends. Learn how you can empower your business to thrive in today’s digital landscape.
- Enterprise cloud security provides the framework to embed security throughout the migration and development lifecycle, ensuring consistent protection as their cloud footprint expands and becomes more integrated into core business processes.
- Identity and access management (IAM) is a cybersecurity discipline that deals with user access and resource permissions.
- These include identity and access management (IAM), regulatory compliance management, traffic monitoring, threat response, risk mitigation and digital asset management.
- Enterprise cloud security is a holistic security discipline that protects an organization’s entire technology value chain across the cloud, not just its network perimeter.
/ Tyre Supplier

/ Latest News
-
MRF TYRES JOIN THE CAMS AUSTRALIAN RALLY CHAMPIONSHIP
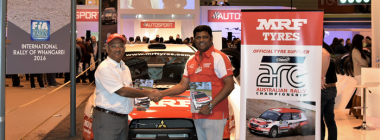
Photo taken at Autosport International with Arun Mammen MD (left) and Vivek Ponnusamy (right). The CAMS Australian Rally Championship® (ARC) Read More >>
-
MRF Tyres success in state and club rally championships
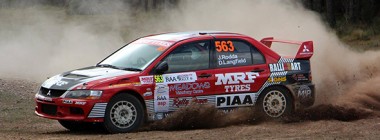
In their first six months in Australia, MRF rally tyres have already had an impact on the sport, with a Read More >>
-
Gaurav Gill wins International Rally of Whangarei
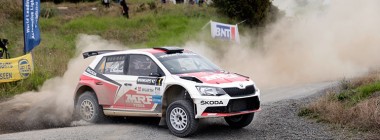
India’s Gaurav Gill and Australian based co-driver Glenn Macneall have won the 2016 International Rally of Whangarei – completing a Read More >>
-
Team MRF back for another shot at APRC
Team MRF will go in search of their eighth Asia-Pacific Rally Championship (APRC) title when the series gets underway in Read More >>
106/52 Dow Street
Port Melbourne 3207
Victoria, Australia
