

Authorised Importer of  for Australia / New Zealand
/ What Is Cyber Resilience?

Attackers motivations can vary for all types of attacks from pleasure to political goals. As with physical security, the motivations for breaches of computer security vary between attackers. Other telecommunication developments involving digital security include mobile signatures, which use the embedded SIM card to generate a legally binding electronic signature. Today many healthcare providers and health insurance companies use the internet to provide enhanced products and services. Smartphones, tablet computers, smart watches, and other mobile devices such as quantified self devices like activity trackers have sensors such as cameras, microphones, GPS receivers, compasses, and accelerometers which could be exploited, and may collect personal information, including sensitive health information.
However, even in highly disciplined environments (e.g., military organizations), social engineering attacks can still be difficult to foresee and prevent. It is possible to reduce an attacker’s chances by keeping systems up to date with security patches and updates and by hiring people with expertise in security. The act of assessing and reducing vulnerabilities to cyberattacks is commonly referred to as information technology security assessments.

Other developments in this arena include the development of technology such as Instant Issuance which has enabled shopping mall kiosks acting https://master-your-business.com/how-can-cybersecurity-protect-your-business/ on behalf of banks to issue on-the-spot credit cards to interested customers. Further developments include the Chip Authentication Program where banks give customers hand-held card readers to perform online secure transactions. Several versions of SSL and TLS are commonly used today in applications such as web browsing, e-mail, internet faxing, instant messaging, and VoIP (voice-over-IP). Related to end-user training, digital hygiene or cyber hygiene is a fundamental principle relating to information security and, as the analogy with personal hygiene shows, is the equivalent of establishing simple routine measures to minimize the risks from cyber threats. A common mistake that users make is saving their user id/password in their browsers to make it easier to log in to banking sites.

Cyber resilience that runs itself with you in the loop
- A cyber resilience framework is a strategy that helps organizations prepare for incoming cyberattacks and protect infrastructure, data, and information systems.
- To achieve cyber resilience, security teams must require authentication, continuous validation, and session monitoring when granting people privileged access to applications and data.
- Customers increasingly want to work with organizations that protect their personal information and avoid service outages.
- That said, there are multiple cyber resilience frameworks that provide high-level guidance.
- Cyber resilience supports digital transformation by allowing organizations to innovate with greater speed, confidence, and security.
- This is because cyber resilience entails identifying potential threats, assessing their impact, and forming concrete actions to address them.
] standardized the penetration test service as a pre-vetted support service, to rapidly address potential vulnerabilities, and stop adversaries before they impact US federal, state and local governments. Office of Personnel Management (OPM), which compromised the records of about 4.2 million current and former government employees. Following cyberattacks in the first half of 2013, when the government, news media, television stations, and bank websites were compromised, the national government committed to the training of 5,000 new cybersecurity experts by 2017.
Business continuity
Hong Kong’s Protection of Critical Infrastructures (Computer Systems) Bill (the “Bill”) was passed by the Legislative Council on 19 March 2025, with the purpose to “establish legal requirements for organisations designated as critical infrastructure operators”. The Canadian Cyber Incident Response Centre (CCIRC) is responsible for mitigating and responding to threats to Canada’s critical infrastructure and cyber systems. The role of the government is to make regulations to force companies and organizations to protect their systems, infrastructure and information from any cyberattacks, but also to protect its own national infrastructure such as the national power-grid. “The malware utilized is absolutely unsophisticated and uninteresting,” says Jim Walter, director of https://expandsuccess.org/protecting-your-financial-information/ threat intelligence operations at security technology company McAfee – meaning that the heists could have easily been stopped by existing antivirus software had administrators responded to the warnings.

/ Tyre Supplier

/ Latest News
-
MRF TYRES JOIN THE CAMS AUSTRALIAN RALLY CHAMPIONSHIP
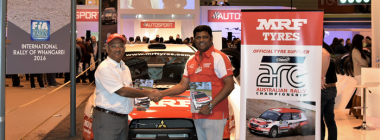
Photo taken at Autosport International with Arun Mammen MD (left) and Vivek Ponnusamy (right). The CAMS Australian Rally Championship® (ARC) Read More >>
-
MRF Tyres success in state and club rally championships
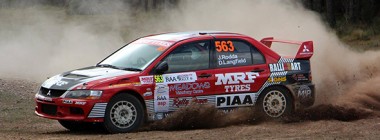
In their first six months in Australia, MRF rally tyres have already had an impact on the sport, with a Read More >>
-
Gaurav Gill wins International Rally of Whangarei
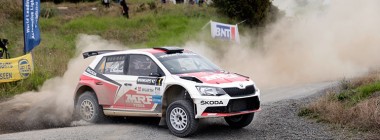
India’s Gaurav Gill and Australian based co-driver Glenn Macneall have won the 2016 International Rally of Whangarei – completing a Read More >>
-
Team MRF back for another shot at APRC
Team MRF will go in search of their eighth Asia-Pacific Rally Championship (APRC) title when the series gets underway in Read More >>
106/52 Dow Street
Port Melbourne 3207
Victoria, Australia
